


Third-party technology is a black box
Supply chain compromise ranked as the second most common initial attack vector and tied for the longest breach lifecycle at 258 days to identify and contain
Manifest secures your software supply chain, from the code you develop to the third-party software and AI you depend on. See what’s inside, continuously identify risk, and respond before it impacts your business.
One platform for Product Security, AI Security, and Third-Party Cyber Risk.
AI coding tools are introducing dependencies faster than security teams can review them. Open-source supply chain attacks are turning trusted developer tools into attack vectors. AI is being embedded inside third-party products with little transparency. And new regulations are forcing organizations to prove what’s inside the technology they build and buy.
Supply chain compromise ranked as the second most common initial attack vector and tied for the longest breach lifecycle at 258 days to identify and contain
31% of breaches now start with a vulnerability exploit, the first time in
19 years it beat stolen credentials
Shadow AI incidents jumped from 20% to 43% of breached organizations in one year, and those breaches cost $5.39 million on average
Open source appears in 98% of codebases, meaning almost every application inherits third-party risk
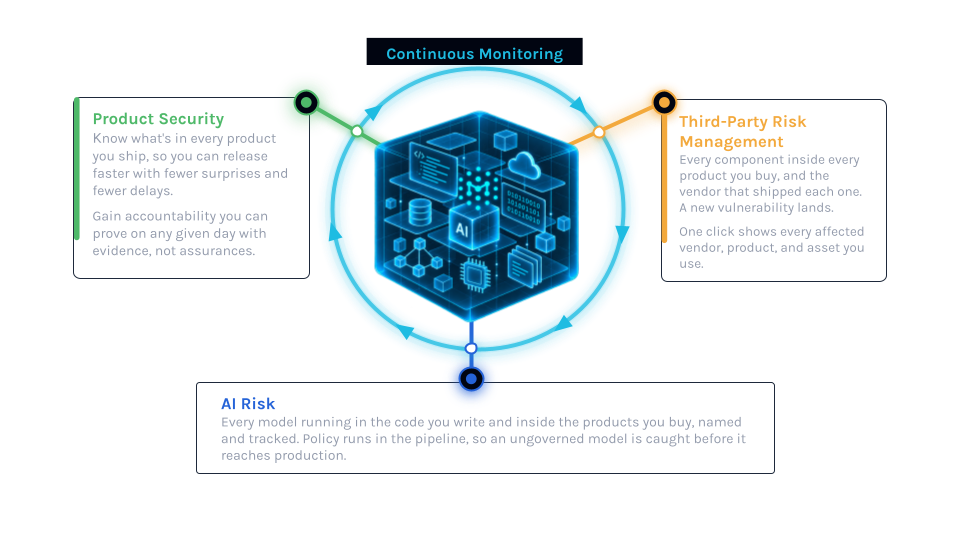
Find where a vulnerable or compromised component exists across your products and suppliers.
Know when new dependencies, vulnerabilities, AI models, or supplier risks enter your environment.
Manage first-party software, third-party technology, and AI supply chain risk in one platform.
Most security tools see only one part of your technology stack. Manifest gives you an inside-out view across source code, binaries, open-source dependencies, supplier software, and AI so security teams can understand and act on risk across the entire software supply chain.
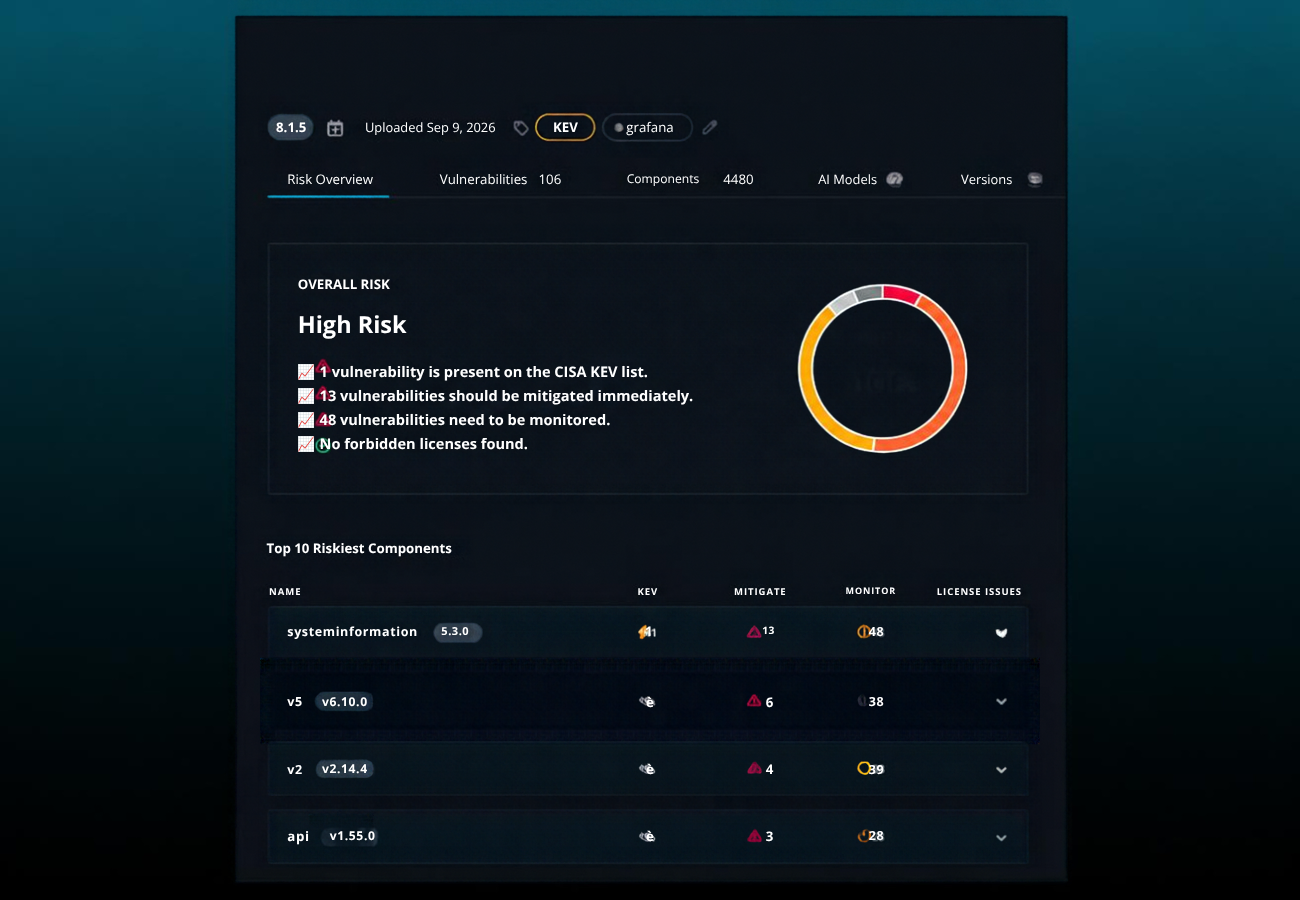
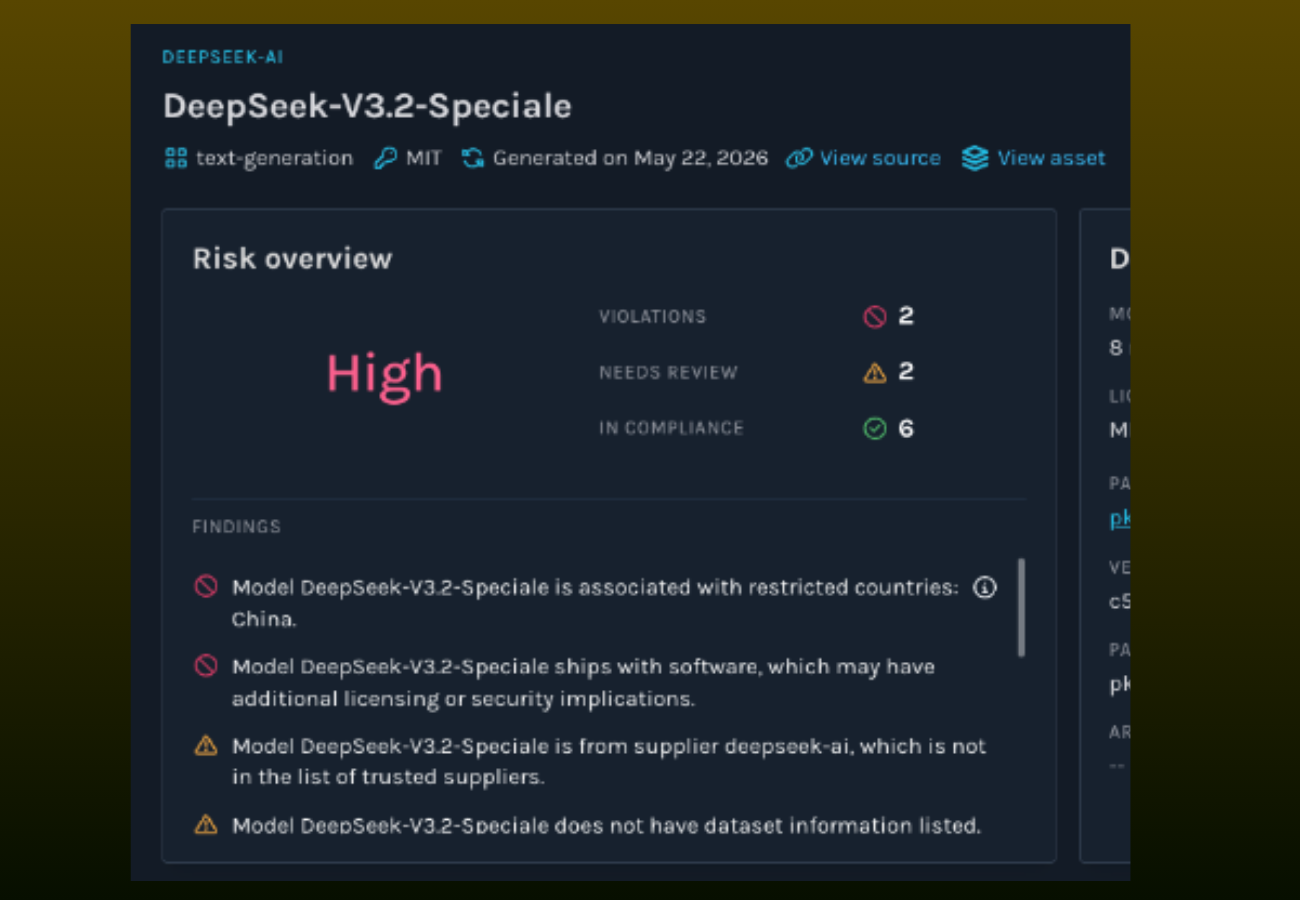
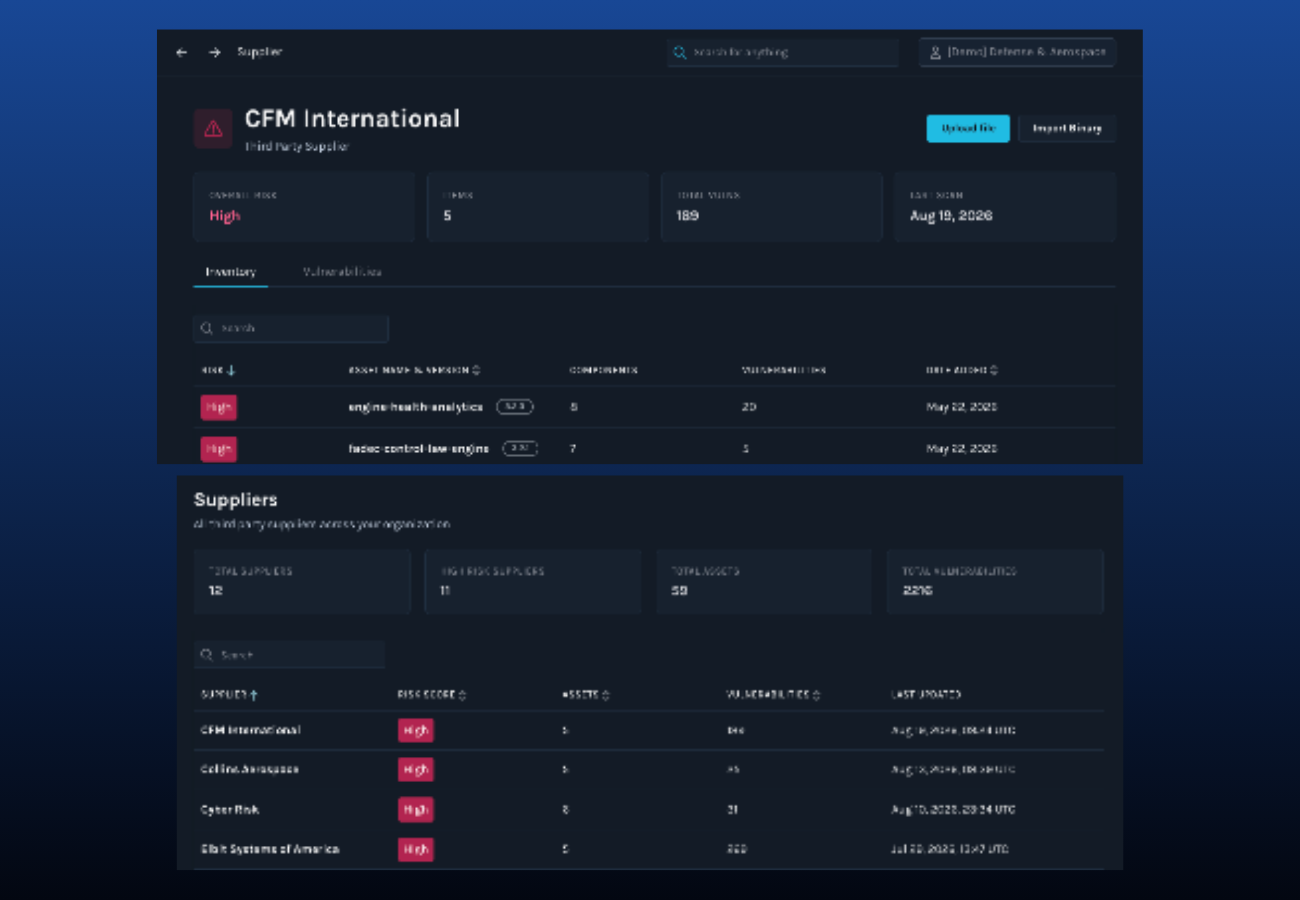
Traditional third-party risk tools rely on questionnaires, certifications, external attack-surface signals, and periodic assessments. Those signals matter—but they don’t tell you what’s actually inside the software running in your environment. Manifest analyzes the technology itself: the packages, dependencies, binaries, vulnerabilities, licenses, provenance, and AI models inside supplier products.
Find every impacted product and supplier in seconds.
Maintain evidence continuously for customers, auditors, regulators, and government agencies.
Analyze supplier SBOMs and binaries instead of relying only on questionnaires.
Prioritize findings using exploitability, reachability, product context, and real-world threat intelligence.
Continuously inventory and assess new components as software changes.
Track models, datasets, provenance, licenses, and associated risk.
Software supply chain security protects the software, open-source components, third-party dependencies, development infrastructure, and AI models your organization builds and relies on. The goal is to understand what is inside your technology, identify meaningful risk, and respond quickly when threats emerge.
Traditional SCA tools primarily scan source repositories for open-source vulnerabilities. Manifest extends visibility to complete products, binaries, containers, supplier software, and AI, helping teams understand risk across the technology they build, deploy, and procure.
Manifest gives security teams direct visibility into supplier technology itself. Teams can analyze vendor SBOMs and binaries, identify vulnerable or risky components, discover embedded AI, and continuously monitor supplier products after procurement.
Yes. Manifest can generate, ingest, validate, enrich, analyze, monitor, and share SBOMs. But SBOMs are one source of evidence within the broader platform—not the end goal. Manifest uses software transparency data to drive security decisions across the full software supply chain.
Manifest inventories AI models and related components, tracks provenance and licensing, evaluates security and compliance risk, and provides visibility into AI used internally and embedded inside third-party products.